2023-01-04 · 2분
Pentest Practice — SQL Injection
A payload cheatsheet from SQLi practice: error-based, union-based, blind, and time-based injection, plus quick notes on sqlmap, hashcat, SSRF bypasses, and Log4j JNDI strings.
securityweb
2021-06-02 · 1분
This post is over 2 years old. The content may be outdated.
It's a site where you can practice the web-hacking technique called XSS.
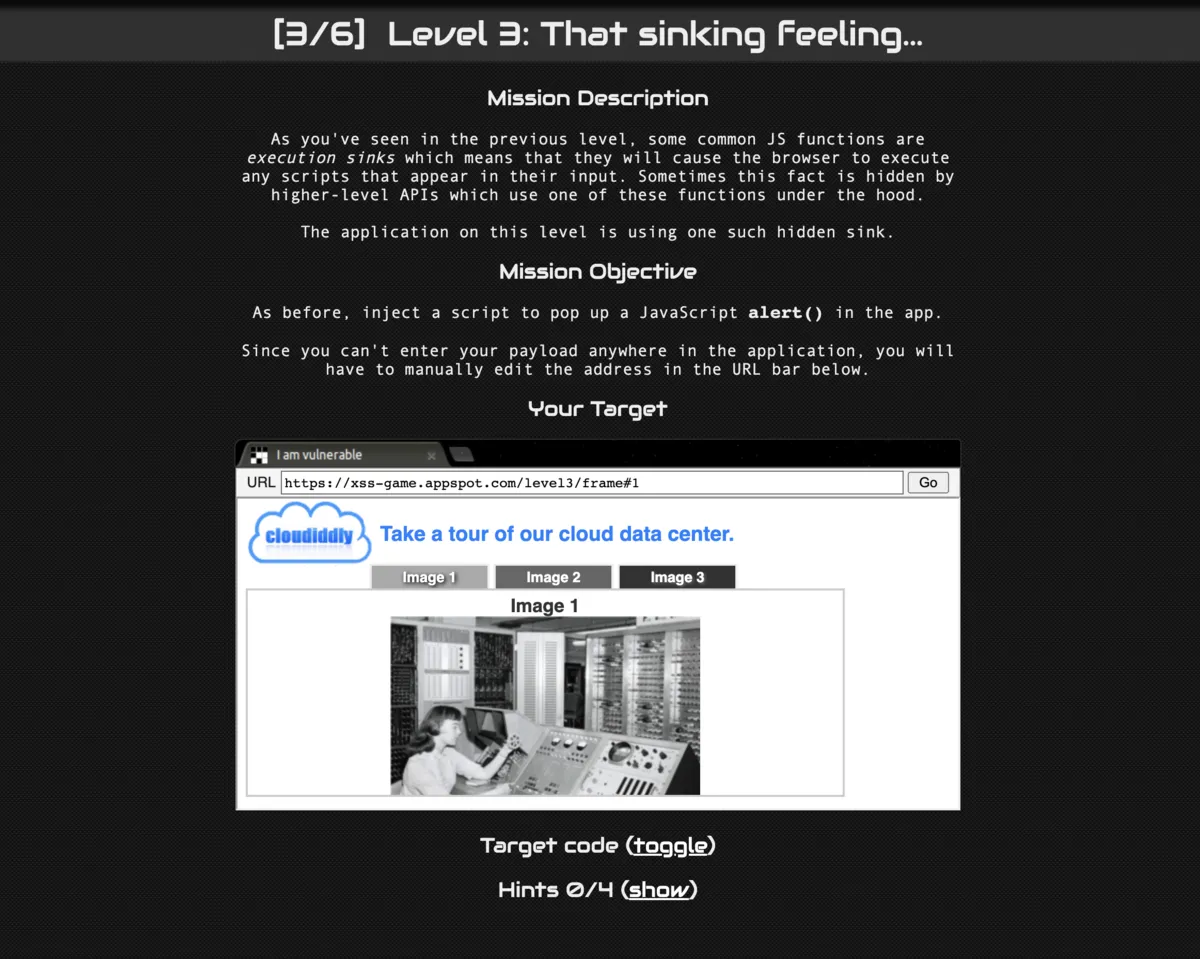
frame#1
Entering level3, this is the screen. First let's press the very clickable Image 1, 2, 3!
frame#2
frame#3
As above, when you press the image button, you can see a number appears after frame# according to that number!
So let's enter 4, which doesn't exist here.
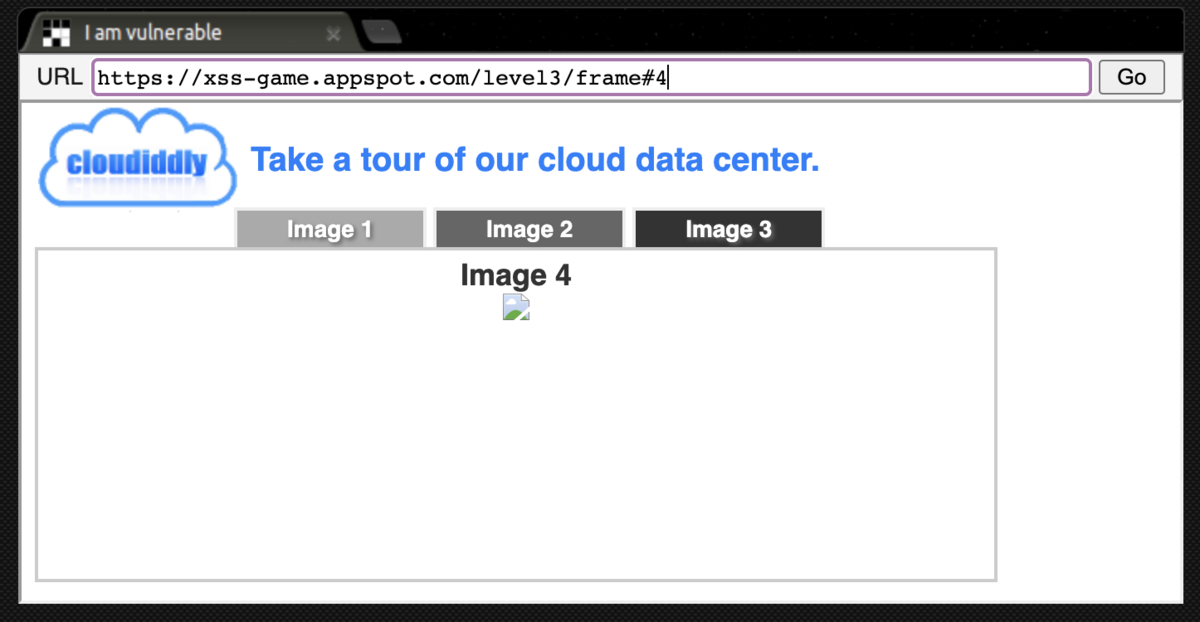
frame#4
Entering it, the image shows up broken. Something showing up as a broken image like that
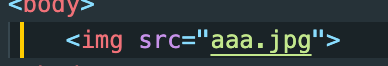
appears in HTML when, when using the img tag, the image doesn't exist at the file path stored in src.
Here we can use onerror, which runs when the image comes out broken — that is, when an error occurs.

For example, writing as above means that when there's no file called aaa.jpg, it runs "alert()".
So let's try entering it as-is.
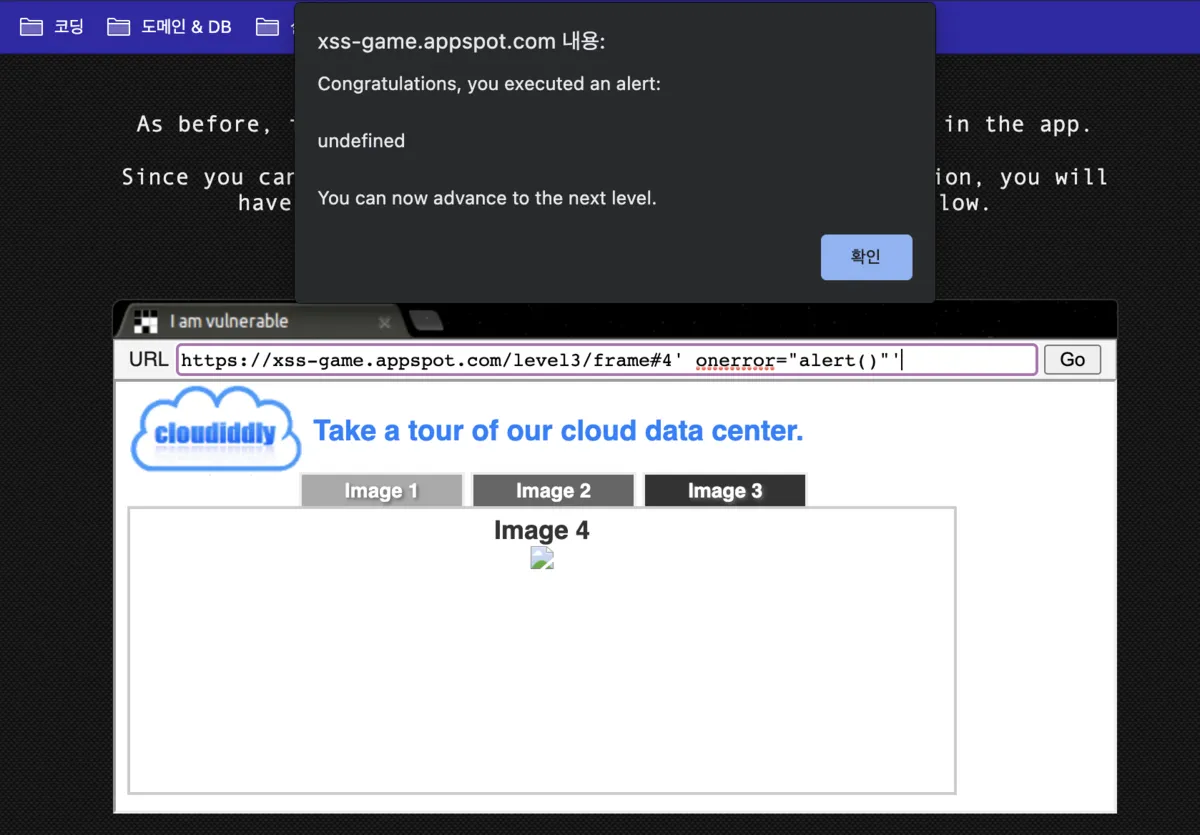
Writing onerror="alert()" into the broken-image frame#4, you can see it runs successfully!!
+Additional


What's important here is the html += "img<>" part of the script. You can see it closes it off as frame# + num + .jpg, and brings the value after # and appends it. So you write it like frame#4.jpg' onerror="alert()"'.
https://unsplash.com/photos/u3ajSXhZM_U
Original (Korean): tistory — published 2021-06-02, migrated to this blog. This translation was generated with the help of AI.
…