What is LOS?
LOS (Lord Of SQLInjection) is a web-hacking practice site where you can practice SQL Injection.
For SQL Injection, please read this post [Hacking/Web hacking] - SQL Injection ~heh.
[Hacking/Web hacking] - [LOS] #2 cobolt write up <- problem #2
Solution process
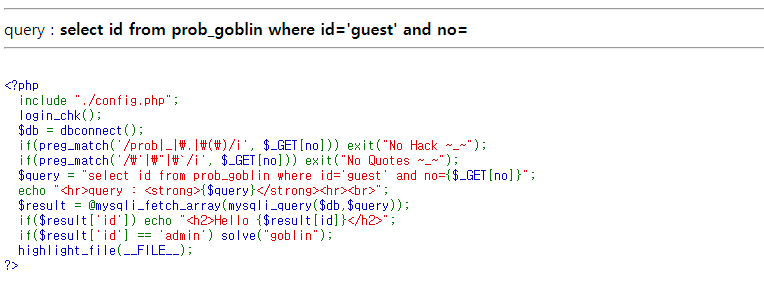
Looking at problem #3, it seems a little different from before!
$query = "select id from prob_goblin where id='guest' and no={$_GET[no]}";
Looking at the query, the id value is fixed to guest, and the part the user inputs seems to be this no= part. And~
if($result['id']) echo "<h2>Hello {$result[id]}</h2>";
if($result['id'] == 'admin') solve("goblin");
This is the part to solve, and it's similar to the previous problem? It seems it's done once the id value becomes admin! So let's input it the same way as before.
When I entered it like no=id=admin%20%23,
special characters seem to be detected like this.
if(preg_match('/\'|\"|\`/i', $_GET[no])) exit("No Quotes ~_~");
So shall we put the basic value 1 into no?
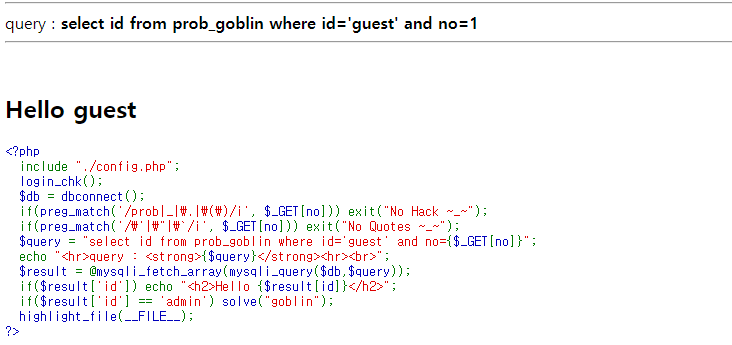
It greets us as guest... we want to become admin, so let's put in a different value. Let's try 2, 3, 4.
!> ****](https://www.easycalculation.com/ascii-hex.php)
Nothing shows up? Seems it's false! So let's write it as below. select id from prob_goblin where id='guest' and no=23 or id='admin' ↳ put a false value in no to make it false, and use or to make the id admin. Oh, but as we tried above, special characters are blocked. So what should we do? The answer is to use ASCII codes. Shall we use them and rewrite it? **select id from prob_goblin
— ascii-hex.php — you can easily obtain ASCII codes on a site like this.
Original (Korean): tistory — published 2021-06-06, migrated to this blog. This translation was generated with the help of AI.